

Internal documents containing the resident registration numbers and bank account numbers of employees and others were leaked from major South Korean music agency SM Entertainment and key affiliates in a security incident. The breach involved unauthorized external access to the company’s systems and was confirmed to have affected affiliates responsible for its fan platform and concert planning as well.
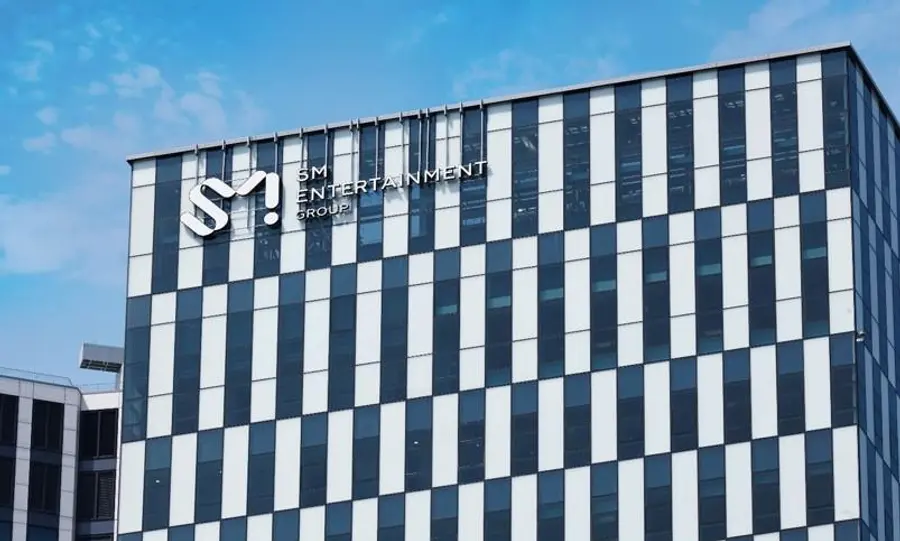
Unauthorized intrusion into electronic approval system confirmed; attack route blocked immediately and in-depth investigation launched
In a notice posted on its official website on the 8th, SM Entertainment said that, during internal security monitoring, it confirmed an external attacker had used unauthorized means to access the company’s electronic approval system and other business networks and had stolen some of the document files stored there.
The investigation found that the breach occurred around the 4th of this month. The leaked information included a large amount of sensitive data, including employees’ resident registration numbers and bank account numbers, as well as mobile phone numbers, addresses, affiliations and information listed in contracts.
The impact was not limited to the head office. Similar signs of data leakage were also found in the computer systems of DearU, the IT affiliate that operates bubble, a global fan communication platform, and Dream Maker, the entertainment company responsible for planning large-scale concerts and performances.
The company said it immediately took defensive measures after detecting signs of unusual activity, including fully blocking the internet protocol (IP) addresses and access routes used in the attack and replacing unauthorized access keys. It has also begun a detailed investigation into the circumstances of the incident and a comprehensive review of its security systems in coordination with relevant government authorities and security experts.
No signs of further harm resulting from misuse of the leaked information have been reported so far. An SM representative said the company takes the incident seriously and will further strengthen access controls and monitoring across its internal network to prevent similar incidents from happening again.
댓글 (0)
댓글 작성
댓글을 작성하려면 로그인이 필요합니다.
로그인하기